Tenable Vulnerability Management
Introduction
This guide tells you how to authenticate the Tenable Vulnerability Management connector in Swimlane using API Key Authentication.
You will generate API keys in Tenable Vulnerability Management, collect the required credentials, and configure the connector in Swimlane.
Prerequisites
Tenable Vulnerability Management Access Requirements
You must have permissions to:
- Access the Tenable Vulnerability Management console.
- Generate API keys.
- Access the Tenable Vulnerability Management API.
- View vulnerability and asset data required by the connector.
Required Credentials
During setup, you will collect:
- Host URL
- Access Key
- Secret Key
Tenable Vulnerability Management Setup
Take the following steps to generate API Keys:
- Log in to your Tenable Vulnerability Management account.
- Click your profile icon in the upper-right corner.
- Select My Account.
- Open the API Keys section.
- Click Generate API Keys.
- Copy and securely save the following values:
- Access Key
- Secret Key
These credentials are used to authenticate the Swimlane connector.
Take the following steps to collect the Host URL:
- Log in to your Tenable Vulnerability Management tenant.
- Copy the URL displayed in your browser.
Example:
https://cloud.tenable.com
Use this value as the url during connector configuration.
Connector Configuration in Swimlane
- Log in to Turbine.
- From the left-hand navigation pane, click ORCHESTRATION and click Assets.
- Asset homepage opens.
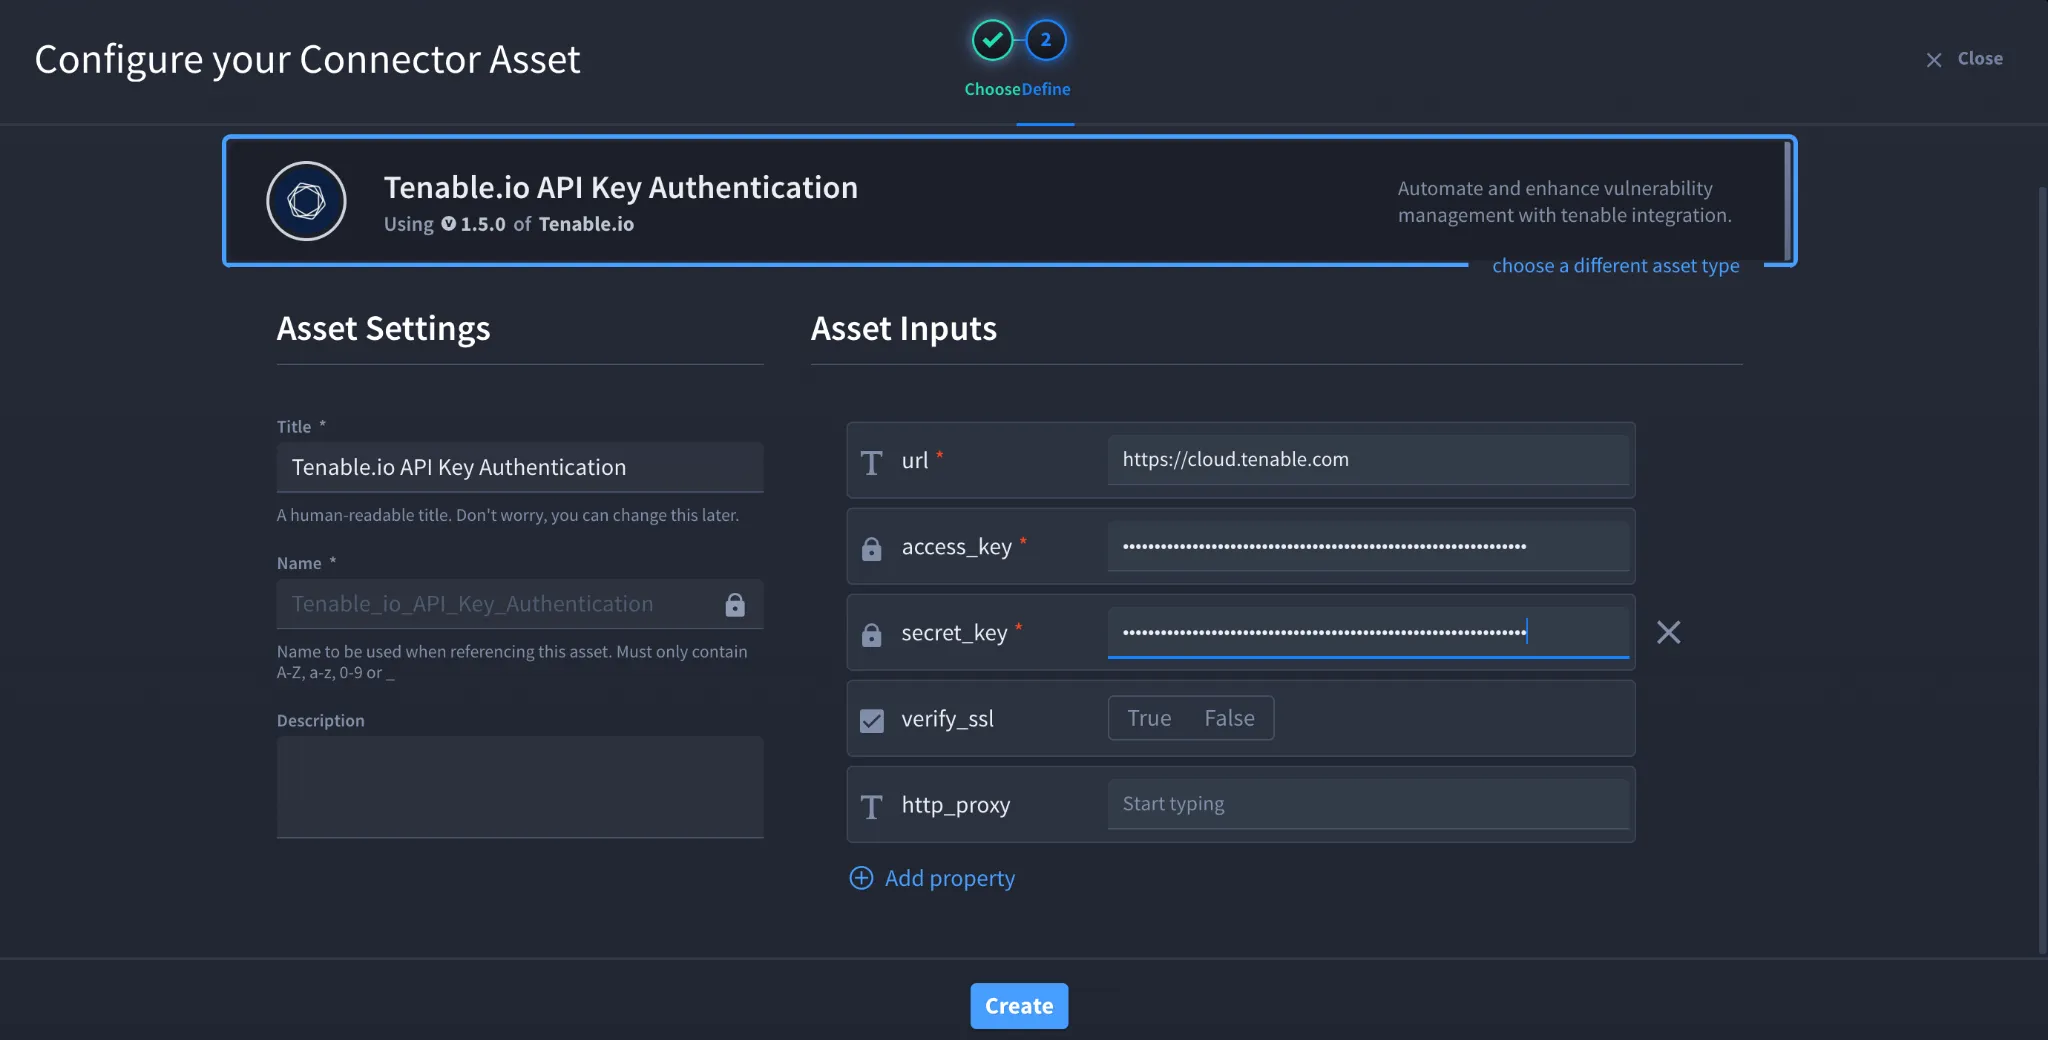
- Click the plus icon to open the Configure your Connector Asset window.
- Select Tenable Vulnerability Management from the Asset type list.
- Fill in the Asset Settings and Asset Input as shown:
Field | Description | Required/Optional |
|---|---|---|
url | Tenable Vulnerability Management Host URL | Required |
access_key | API Access Key generated in Tenable | Required |
secret_key | API Secret Key generated in Tenable | Required |
verify_ssl | Enable/Disable SSL Verification | Optional |
http_proxy | Optional proxy configuration | Optional |
Fields with * marks are required.
- Click Create.
Troubleshooting
Authentication Failed (401 Unauthorized)
Verify that:
- The Access Key is correct.
- The Secret Key is correct.
- The API keys have not been regenerated or revoked.
- The Host URL is correct.
Permission Denied (403 Forbidden)
Verify that:
- Your Tenable account has permission to access the requested resources.
- The API keys belong to a user with sufficient privileges.
- Your account has access to the required assets, scans, and reports.
Unable to Connect
Verify that:
- The Host URL is reachable from the Swimlane instance.
- Firewall or proxy settings allow outbound HTTPS traffic.
- The Tenable service is available.
SSL Errors
If SSL verification fails:
- Verify that the Tenable endpoint uses a trusted SSL certificate.
- Confirm that any proxy is not intercepting SSL traffic.
- Disable verify_ssl only for testing if permitted by your organization's security policy.
Result
You have successfully authenticated the Tenable Vulnerability Management connector in Swimlane.
Sources
- Tenable Developer Portal – Generate API Keys https://developer.tenable.com/docs/authorization
- Tenable Vulnerability Management API Documentation https://developer.tenable.com/reference
- Tenable Workbench Filters Documentation https://developer.tenable.com/docs/workbenches-filters
- Tenable Vulnerability Management User Guide https://docs.tenable.com/vulnerability-management/