Cofense Triage
Introduction
This guide tells you how to authenticate the Cofense Triage connector in Swimlane using OAuth 2.0 Client Credentials.
You will generate API credentials in Cofense Triage, collect required identifiers, and configure the connector in Swimlane.
Prerequisites
Cofense Triage Access Requirements
You must have access to:
- Cofense Triage platform (with administrative privileges)
- API access enabled for your account
- Permission to generate API tokens and OAuth credentials
Required Credentials
During setup, you will collect:
- URL (Cofense Triage API endpoint)
- Client ID
- Client Secret
- API Token (generated in Cofense Triage)
Cofense Triage Setup
Take the following steps to generate an API Token:
- Log in to the Cofense Triage platform.
- Navigate to: Administration → Account Management → Operators
- Locate the superuser account that will be used for API access.
- In the API Token Actions column, click the (+) icon.
- Copy the generated API token and store it securely.
This token will be used along with your account credentials for authentication.
Take the following steps to obtain OAuth Credentials:
- Ensure your application is registered with Cofense Triage.
- Retrieve the following from your Cofense environment:
- Client ID
- Client Secret
- Confirm API access is enabled for your account.
API Endpoint Format
The general Cofense Triage API URL format is: https://<hostname>/api/public/v2/
Example: https://your-instance/api/public/v2/reports
Connector configuration in Swimlane
- Log in to Turbine.
- From the left-hand navigation pane, click ORCHESTRATION and click Assets.
- Asset homepage opens.
- Click the plus icon to open the Configure your Connector Asset window.
- Select Cofense Triage from the Asset type list.
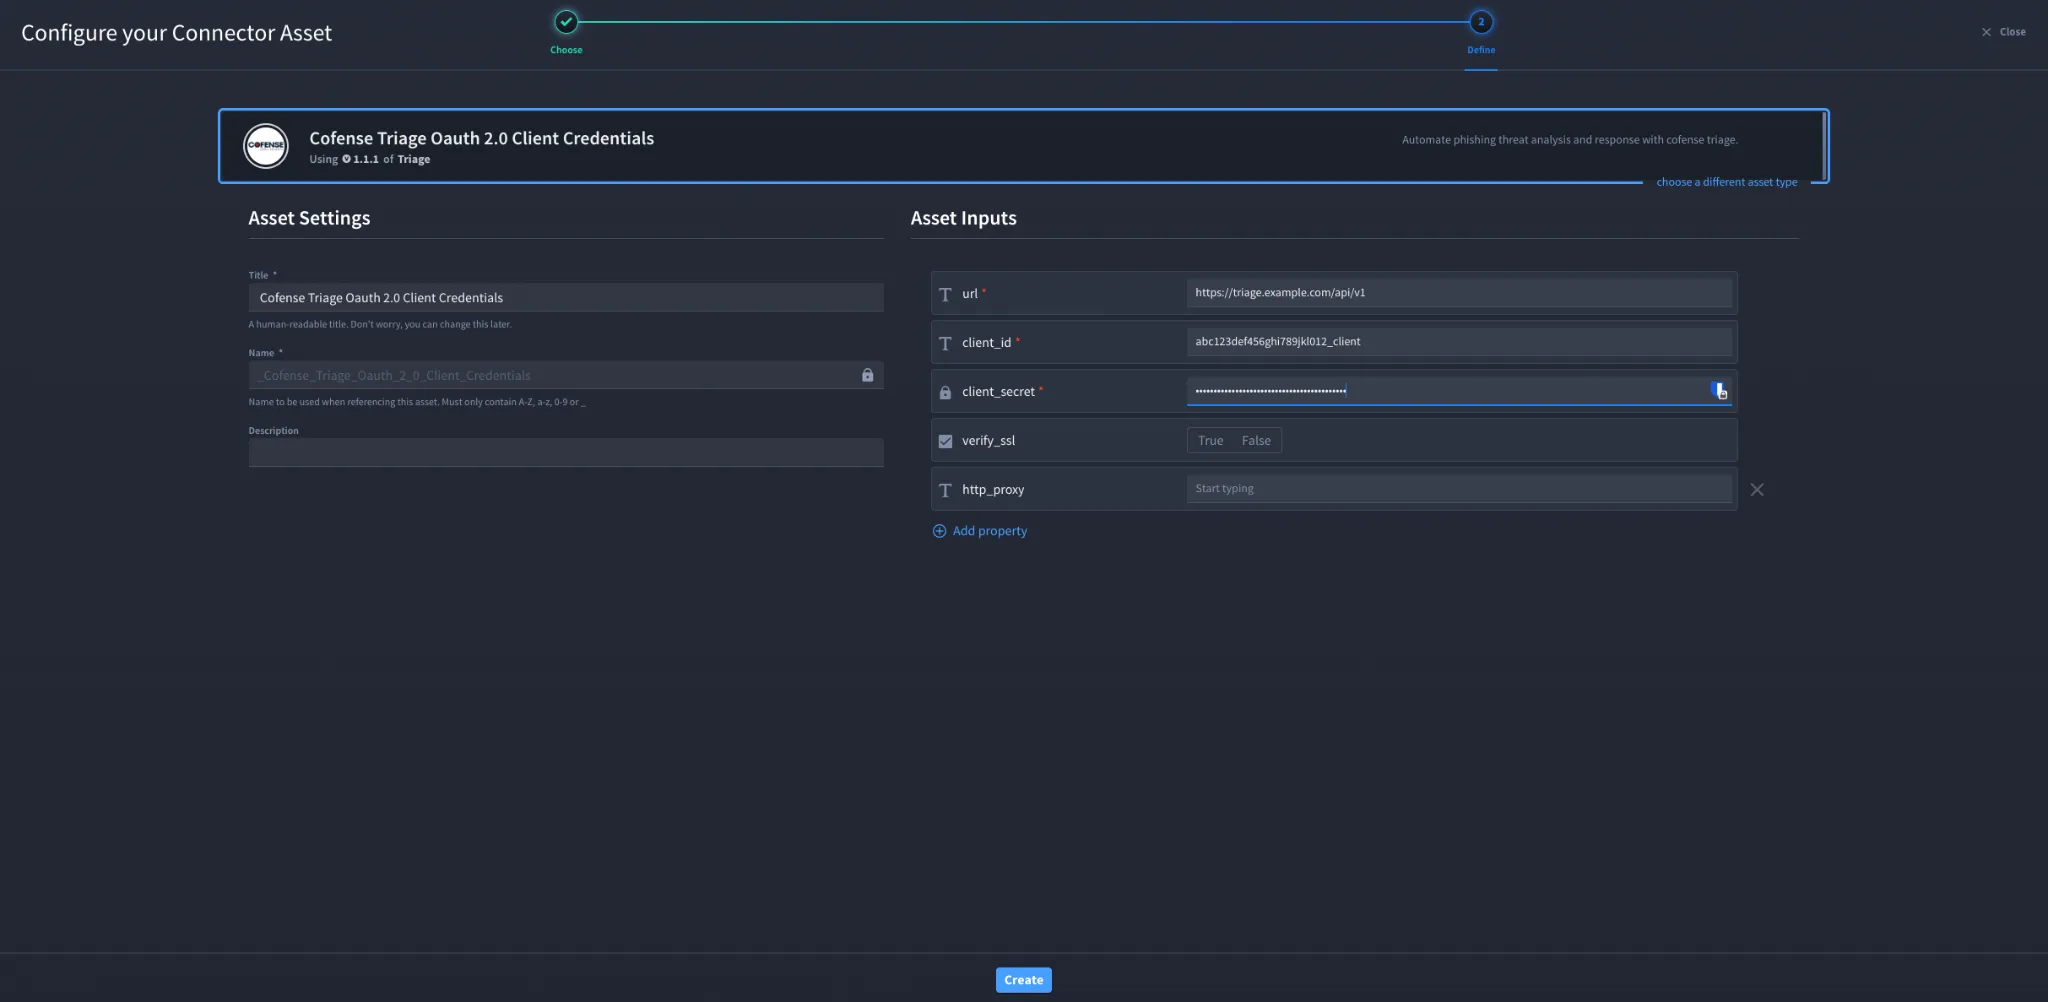
- Fill in the Asset Settings and Asset Input as shown:
Configuration - OAuth 2.0 Client Credentials
Field | Description | Required/Optional |
|---|---|---|
url | Cofense Triage API base URL | Required |
client_id | Client ID from Cofense | Required |
client_secret | Client Secret from Cofense | Required |
verify_ssl | Enable/Disable SSL Verification | Optional |
http_proxy | Optional proxy configuration | Optional |
Fields with * marks are required.
Troubleshooting
If authentication fails:
- Ensure the API token is valid and active
- Verify Client ID and Client Secret are correct
- Confirm the API base URL is correct
- Ensure your account has API access permissions
- Check for network/proxy restrictions
- Verify SSL settings if connection issues occur
You have successfully authenticated the Cofense Triage Connector in Swimlane.
Sources
- Cofense Triage API Documentation : https://community.cofense.com