Setting Up Session Timeout Parameters
As an administrator, you control the amount of time a Swimlane session can be active before the user is forced to re-authenticate, or log out and log back in.
To set up session timeout parameters:
- From the Sessions and Security dashboard, click > to expand the Session controls.
Specify the length and the unit of time to be used to measure the user session and click Save.
Use the drop-down to specify the Session Unit, Hour(s) or Minute(s).
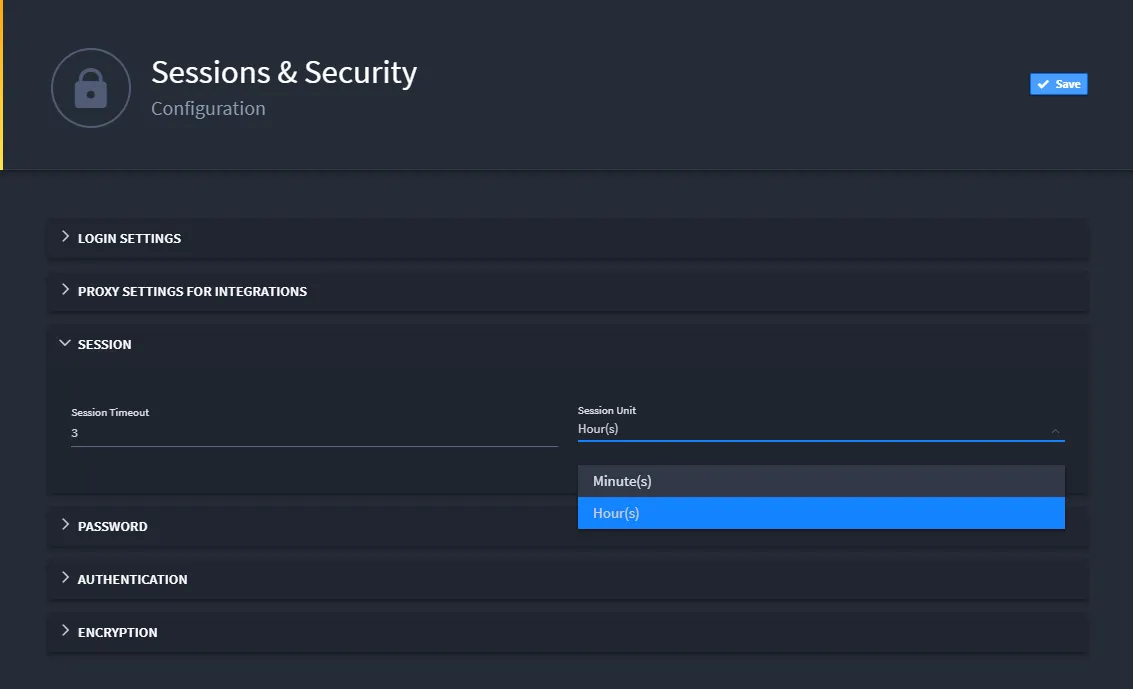
When you adjust the timeout session parameters here, be aware that users will need to log out and back in in order to for the updated time frame to apply. All user sessions will have the previously-set timeout value until their current sessions expire or they log out and log back in.
Overriding a User's Session Timeout
Administrators can override a specific user's session timeout. This is helpful, for example, when you use one Swimlane session as a dashboard for a work area. The dashboard is useful and visible to many people on the team, and you don't want that dashboard to session to timeout frequently. It can also be helpful when you need to immediately disable a user's session. In cases similar to these, you can override the user's session timeout.
To override a user's session timeout:
- From the global navigation menu, select Users, Groups & Roles, and then select Users.
- On Users, select the user whose session timeout you want to override.
On the user's profile settings, click the Session tab.
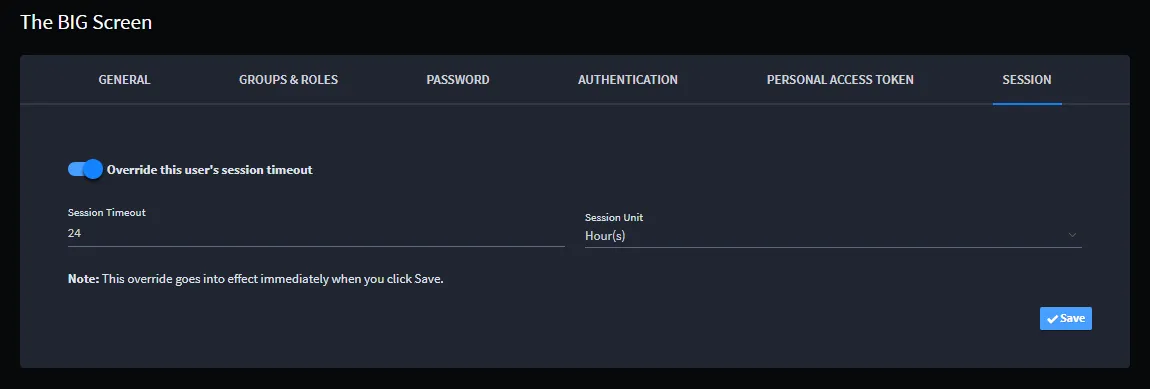
- Toggle the Override this user's session timeout switch, and then specify the time-frame for the override (minutes, or hours).
The minimum you can specify for this override is 1 minute. The maximum is 5 years (43800 hours or 2628000 minutes).
- Click Save.
The override goes into immediate effect once you click save.