Turbine Login and Authentication Methods
Swimlane Turbine supports multiple login methods, depending on how authentication is managed within your organization. The following sections provide an overview of each supported login method.
On-Prem (Turbine 26.3.0): Administrators can customize the text in the welcome area of the login page (next to the sign-in form). To configure it, see Welcome MessageWelcome Message under Account Settings > General. That topic covers HTML support, the default message, and how to clear a custom message.
- Single Sign-On (SSO): You can sign in to Turbine using SSO in two ways: Identity provider (IdP)-initiated or Service Provider (SP)-initiated. Both methods use SAML 2.0 for authentication through an external IdP.
- Login starts directly from the Identity Provider portal (for example, Okta, JumpCloud, Google Workspace, and so on).
- The IdP authenticates the user and redirects to Turbine.
- Login starts from the Turbine application (for example, https://us1.swimlane.app).
- Provide an Account Alias which enables Turbine to determine which IdP to redirect the user to.
- The IdP authenticates the user and redirects to Turbine
- Authentication is handled by the external LDAP directory (for example, Microsoft Active Directory or OpenLDAP).
- Credentials are validated against the directory, and access is granted upon successful authentication.
- Credentials are stored directly within Turbine.
- When a user logs in, Turbine authenticates the users.
After an inactivity timeout or a manual logout, the user is redirected to the same page they were on before. This behavior is user-specific and ensures each user is logged back into their last visited page in the application.
Identity Provider (IDP)-Initiated SSO Login
IdP-initiated SSO begins from your organization's identity provider portal (for example, Okta, JumpCloud, or Google Workspace). After you select the Turbine app, the IdP authenticates your credentials and redirects you to Turbine.
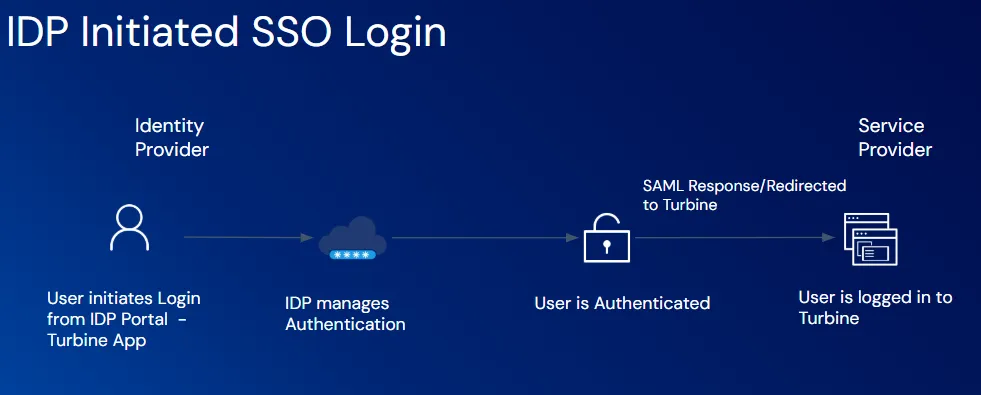
To sign in using IdP-initiated SSO:
- Sign in to your organization's IdP portal.
- Select the Turbine application.
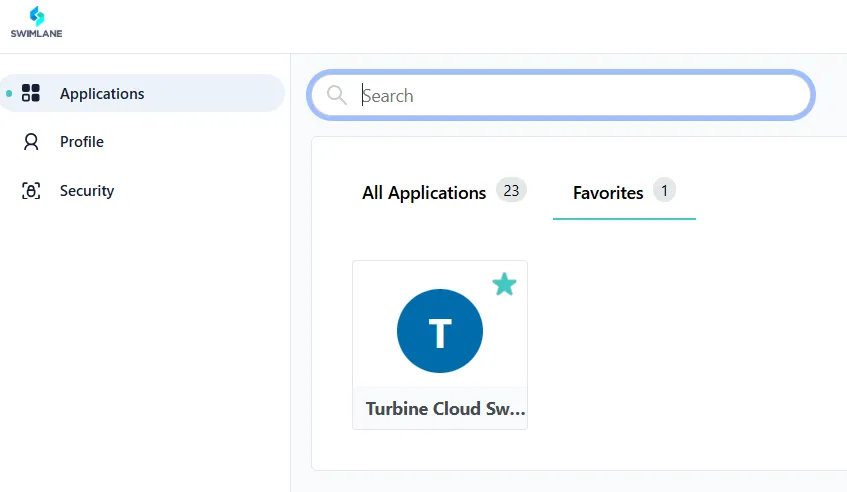
- If Multi-Factor Authentication (MFA) is required, complete the verification(Optional).
- Turbine validates the response, and logs you in.
Service Provider (SP)-Initiated SSO Login
SP-initiated SSO begins from the Turbine login page. Enter your alias or email address, then Turbine routes you to the correct IdP for authentication.
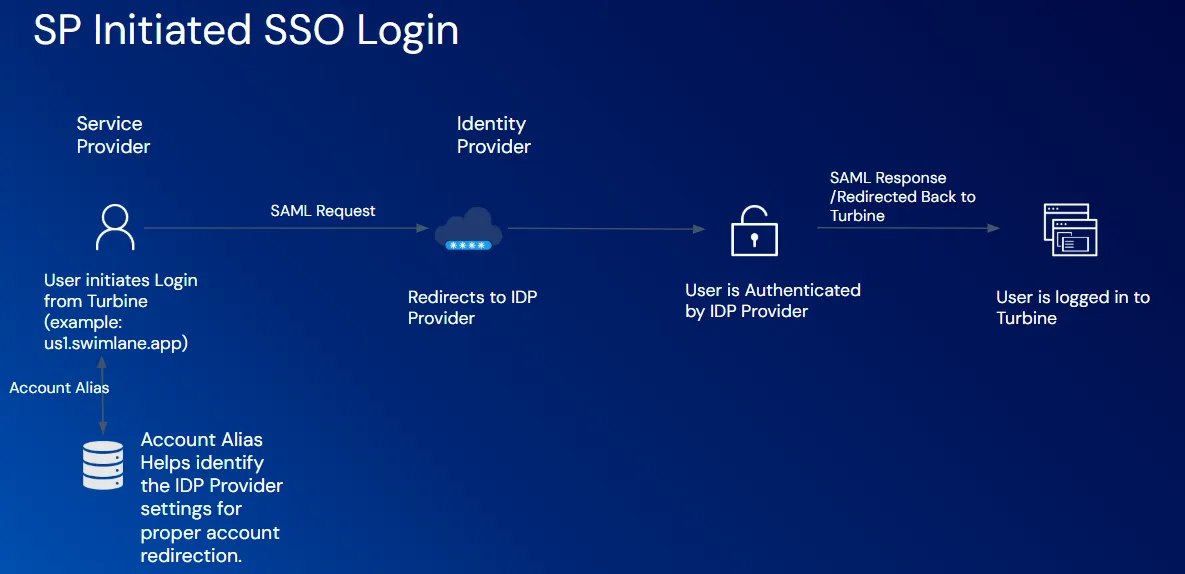
Steps to log in via SP-initiated SSO:
- Navigate to Turbine (for example, https://us1.swimlane.app).
- Select Login via SSO.
- Enter your alias or email address:
- Alias — routes login to the SSO configuration with that alias.
- Email address — Turbine looks up your account and uses your mapped SSO configuration.
Some accounts show Alias only (alias-only login mode).
- When redirected to your IdP, sign in using your IdP credentials.
- If Multi-Factor Authentication (MFA) is required, complete the verification.
- Turbine validates the response and logs you in.
What Is an Account Alias?
An account alias is a short, unique string assigned to an SSO configuration in Turbine. Turbine uses it to identify which IdP to use during SP-initiated login when the user enters an alias instead of an email address.
Why Use an Account Alias?
- Routing to the correct IdP when multiple SSO providers are configured
- Simplified user experience — users enter the alias and Turbine directs them to the correct login provider
Configure the Alias (Admin Only)
To configure an alias for SAML-based SSO:
- Navigate to Settings > Account > Account Settings.
- Open the Sessions & Security tab.
- Expand Authentication, turn Enable on under SAML Authentication, and click SAML Settings.
- Enter the Alias in the SAML Authentication dialog.
- Complete the remaining IdP and service provider fields, click Apply, then click Save on Account Settings.
For the full procedure, see Enable SAML for SSOEnable SAML for SSO.
LDAP Login
LDAP login allows authentication using credentials stored in an external LDAP directory, such as Microsoft Active Directory or OpenLDAP. Turbine connects to the configured LDAP server using the LDAP protocol to validate credentials.
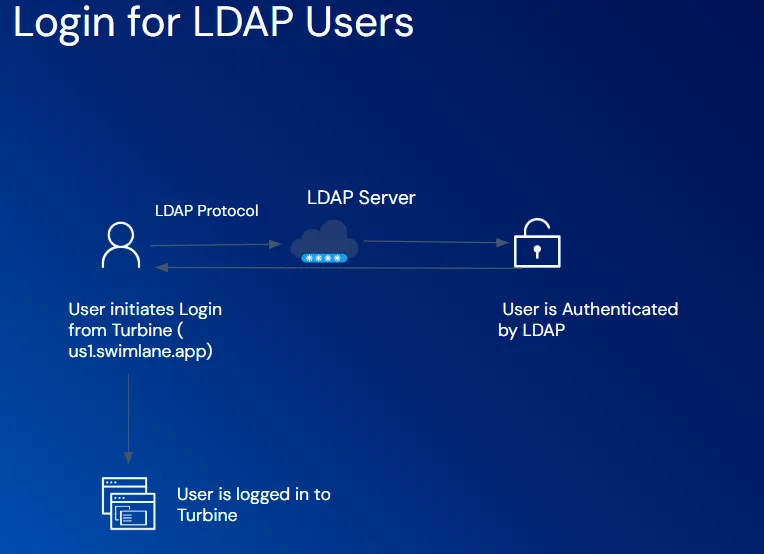
To sign in using LDAP:
- Go to https://us1.swimlane.app.
- Enter your LDAP username or email address and password.
- Turbine connects to the LDAP server to validate your credentials.
- If Multi-Factor Authentication (MFA) is required, complete the verification.(Optional)
- Turbine validates the response, and logs you in.
Application-Managed Login
Application-managed login is handled entirely within Turbine. Credentials are stored and verified by the application, without relying on an external identity provider.
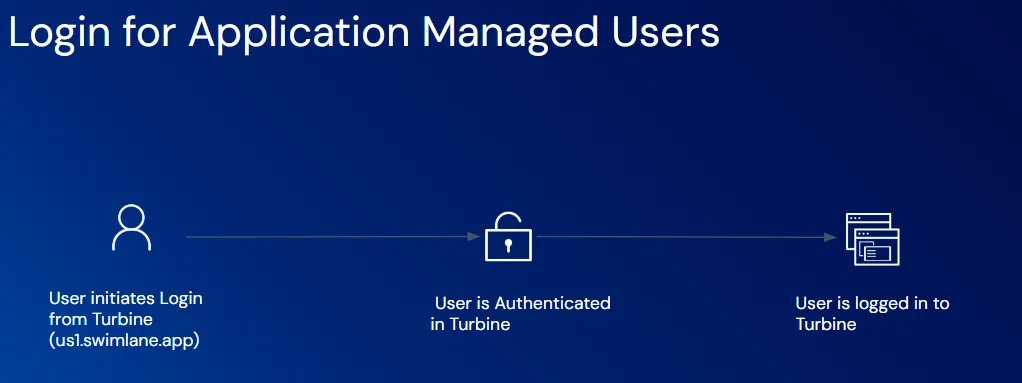
To sign in as an application-managed user:
- Go to https://us1.swimlane.app.
- Enter your registered email address or username and password.
- Turbine validates your credentials.
- If Multi-Factor Authentication (MFA) is required, complete the verification.(Optional).
- Turbine validates the response, and logs you in.
Resetting a Forgotten Password
If you forget your password:
- On the login screen, click Forgot Password?.
- Enter your registered email address.
- Check your inbox for the password reset email.
- Follow the link to create and confirm a new password.
- Return to the login screen and sign in with the new password.
See Also
- Welcome MessageWelcome Message — customize the On-Prem login page welcome area (Account Settings > General > Login Experience)
- GeneralGeneral — Account Name, Domain, and Custom Domain
- Account Settings OverviewAccount Settings Overview