Installing SOC Solutions Bundle
The SOC Solutions Bundle is a solution bundle that is made of four smaller, interconnected solutions: Phishing Triage, Alert Triage, Threat Intelligence (TI), and Case and Incident Management (CIM). For more information, see the corresponding sections.
This installation and configuration documentation is for the Canvas version of the SOC Solutions Bundle only.
The SOC Solutions Bundle is not available in Swimlane Content or the Marketplace. To install it, request the SSP from your Swimlane representative, then import the package.
Important Definitions
- Ingestion Component - A component or set of components that:
- Interact with a vendor endpoint, such as run a SIEM search, look up observable reputation, or initiate a remediation action
- Normalize inputs and outputs using interfaces to enable swappable component usage
- Convert various 3rd-party alerts, reputations, emails, and so on to a common schema for use in Turbine solutions such as SOC Solutions
- Turbine Extendable Data Schema (TEDS) - Turbine's native common schema for interacting with alerts, emails, reputations, and so on.
Request and Import the Package
To install the SOC Solutions Bundle, request the SSP from your Swimlane representative.
After you have the SSP:
- Import the package into your tenant. For steps, see Import Swimlane Solution Packages.
- If the import prompts you to overwrite content that already exists in your environment, review the selection. You can deselect items you do not want to overwrite. If you deselect too many items, the solution may not import completely.
- Enable playbooks and webhooks after import if they remain disabled.
- Reconfigure credentials, key store values, and secure asset fields as required.
Once you have imported the SOC Solutions Bundle, configure it to ingest data from your tools for your use cases.
- For SIEM, XDR, or EDR Alert Triage, see SOC - Alert Ingestion (Cron) - Template Playbook OverviewSOC - Alert Ingestion (Cron) - Template and SOC - Alert Ingestion (Webhook) - Template Playbook OverviewSOC - Alert Ingestion (Webhook) - Template.
- For Phishing Triage, see SOC - Bulk Ingest Phishing Emails - Template Playbook OverviewConfigure Phishing Email Ingestion.
- After you configure one or more alert sources, you can add Threat Intelligence to enhance your observables. See Configure Threat Intelligence Enrichment IntegrationConfigure Threat Intelligence Enrichment Integration.
- You can then configure CIM for your environment. See Configure Custom Case and Incident Management Data MappingsCase and Incident Management Application.
Configure Included Assets
In order to use 3rd party tools for ingestion, enrichment, and so on, you must configure the assets for the tools you wish to use:
- Navigate to Orchestration -> Assets.
- Configure all supplied assets for 3rd-party technologies you wish to use, that is, VirusTotal, Recorded Future, Abuse.ch URLHaus, IPQualityScore.
Configure Custom Assets
The SOC Solutions Bundle contains a number of custom assets whose purpose is to allow you to configure variables used in one or more playbooks or components without having to edit those playbooks or components directly:
- Open the Observable Parser Ignore Lists asset.
- Enter CSV lists of IP CIDR ranges and Domains you wish to exclude from observable ingestion, for example:
- mycompany.com, outlook.com, swimlane.com, o365.com.
- 10.0.0.0/8, 192.168.0.0/16, 172.16.0.0/12.
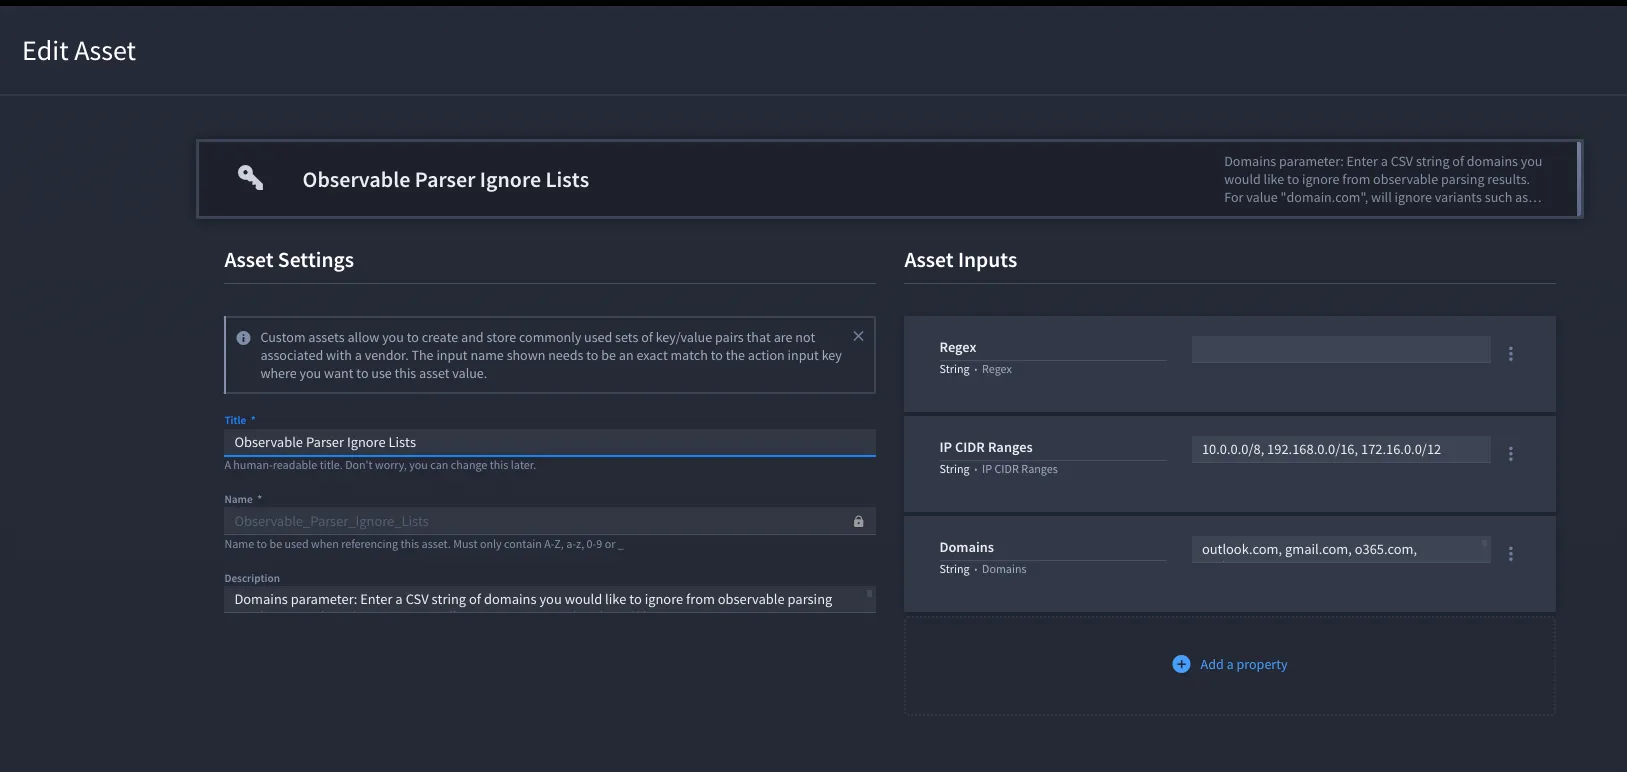
- Open the TI Primary Intelligence Providers asset.
- If you wish to change the primary provider for any TI types, do so here.
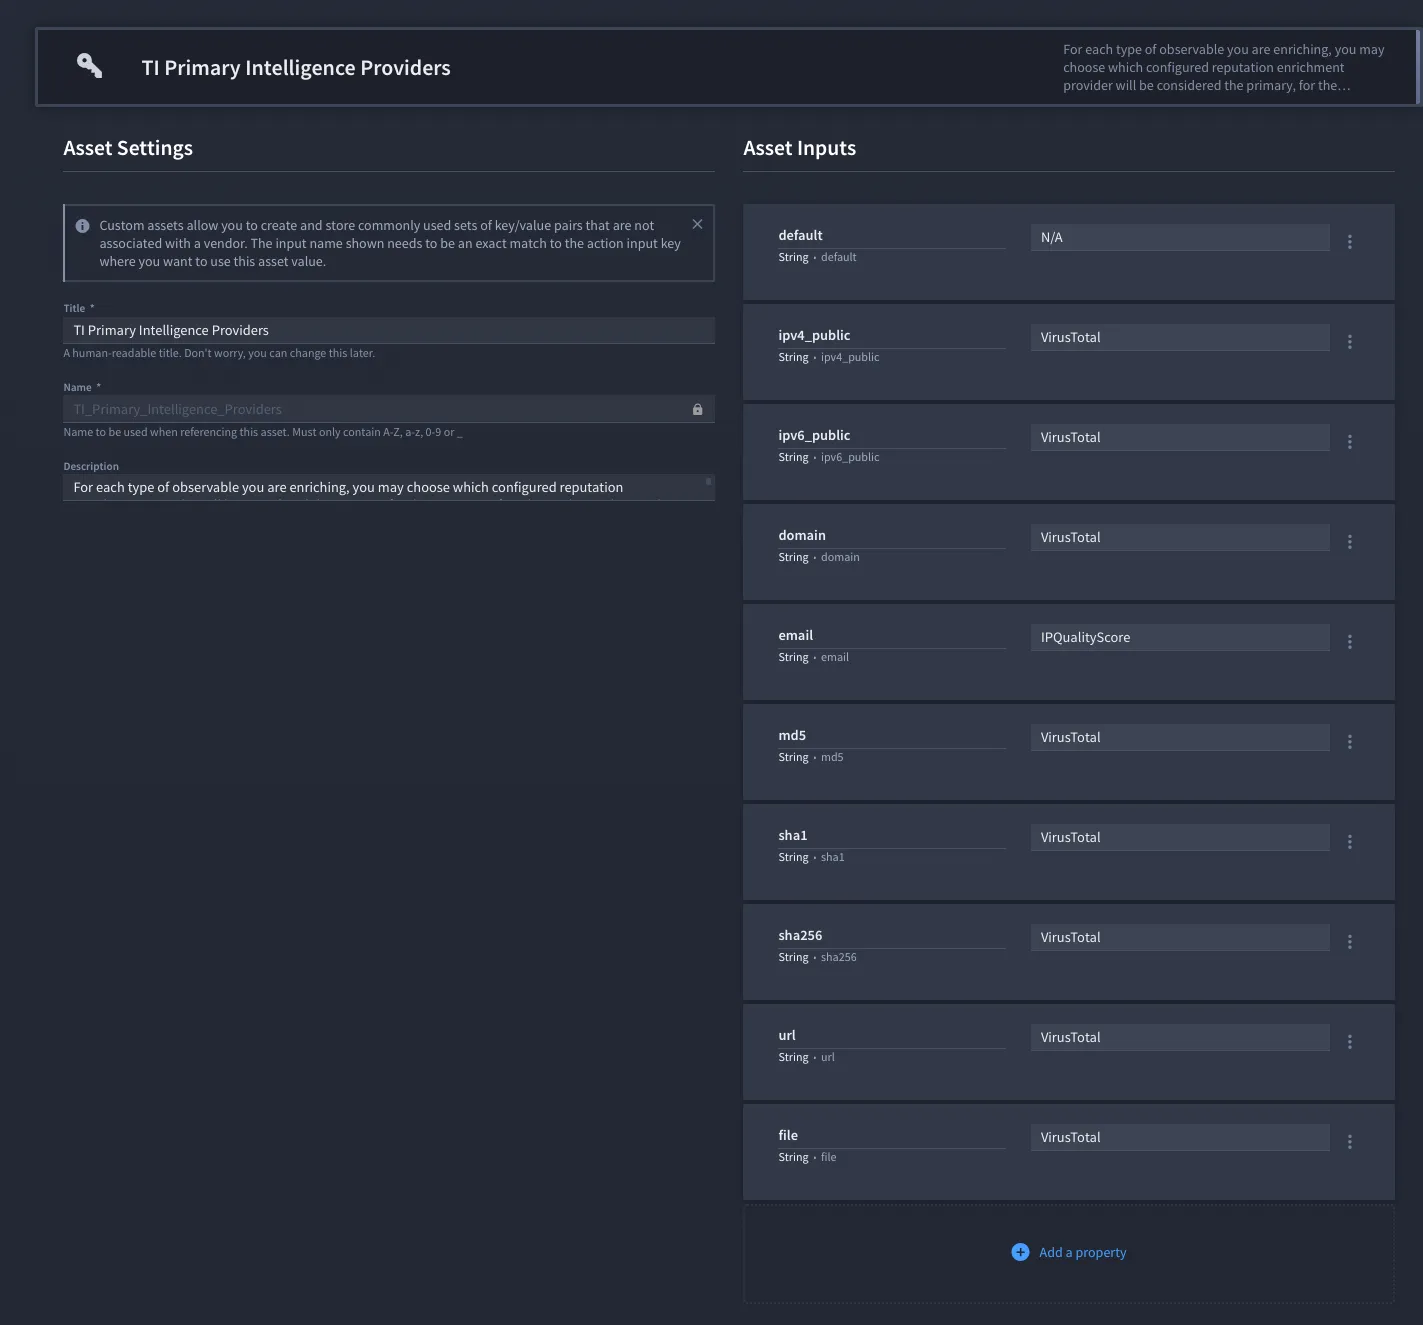
There must be valid and configured enrichment sources. For more information, see Configure Threat Intelligence Enrichment IntegrationConfigure Threat Intelligence Enrichment Integration.