SecureWorks Taegis XDR
Introduction
This guide tells you how to authenticate the SecureWorks Taegis XDR connector in Swimlane using OAuth 2.0 Client Credentials.
You will create an API Client in Taegis XDR, collect the required credentials, and configure the connector in Swimlane.
Prerequisites
SecureWorks Taegis XDR Access Requirements
You must have permissions to:
- Access the SecureWorks Taegis XDR portal.
- Create and manage API Clients.
- Access the Taegis GraphQL API.
- Manage OAuth applications.
Required Credentials
During setup, you will collect:
- Host URL
- Client ID
- Client Secret
- (Optional) OAuth Scope
SecureWorks Taegis XDR Setup
Take the following steps to create an API Client:
- Log in to the SecureWorks Taegis XDR portal.
- Navigate to Administration > API Clients.
- Click Create API Client.
- Enter a name and description for the API client.
- Assign the required API permissions based on the actions you want the connector to perform.
- Click Create.
- Copy and securely save the Client ID.
- Copy and securely save the Client Secret.
These values are used to authenticate the Swimlane connector.
Take the following steps to collect the Host URL:
- Log in to your SecureWorks Taegis XDR tenant.
- Copy the tenant URL from your browser.
Example:
https://api.<region>.taegis.secureworks.com
Use this value as the url during connector configuration.
OAuth Scope
The Swimlane connector supports an optional scope parameter. If your SecureWorks administrator specifies OAuth scopes for your API client, enter them in the connector configuration. Otherwise, leave this field blank.
Connector Configuration in Swimlane
- Log in to Turbine.
- From the left-hand navigation pane, click ORCHESTRATION and click Assets.
- Asset homepage opens.
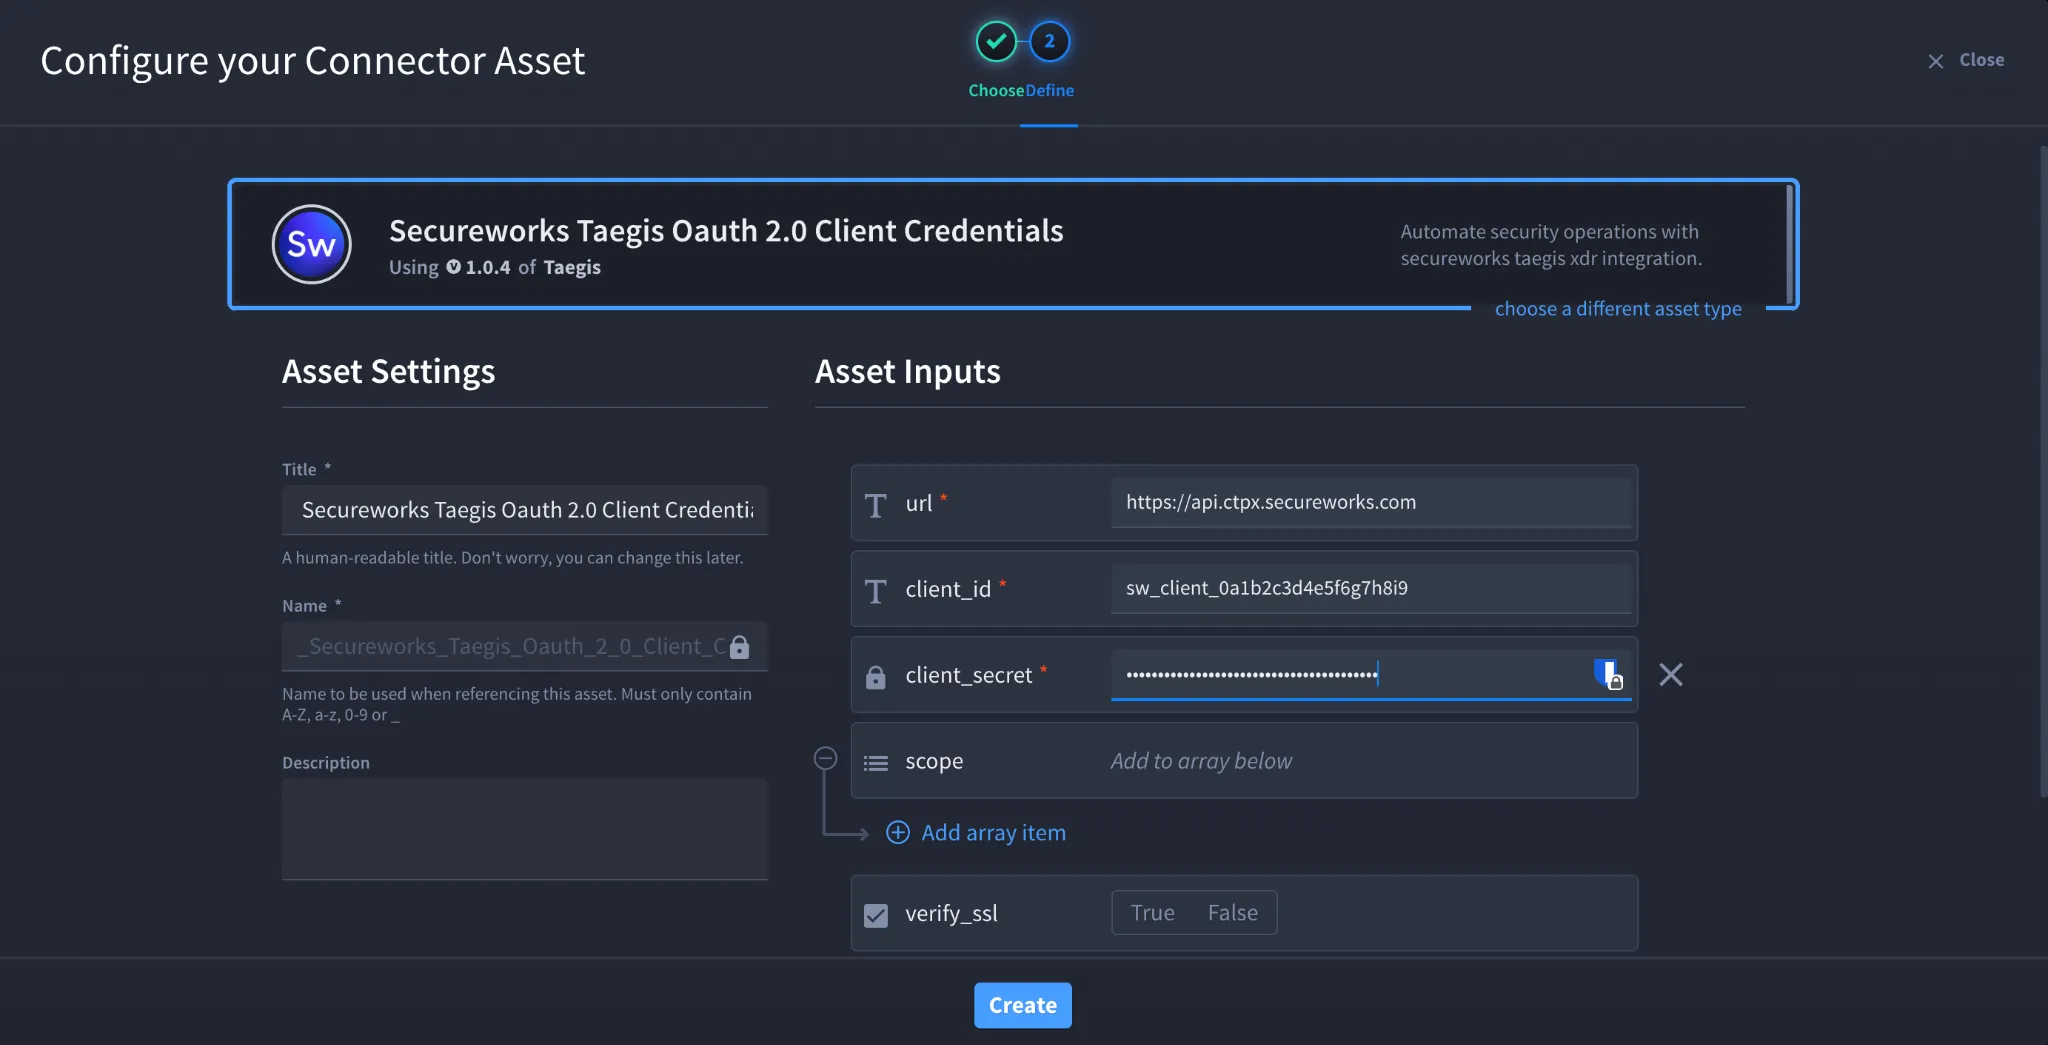
- Click the plus icon to open the Configure your Connector Asset window.
- Select SecureWorks Taegis XDR from the Asset type list.
- Fill in the Asset Settings and Asset Input as shown:
Field | Description | Required/Optional |
|---|---|---|
url | SecureWorks Taegis XDR Host URL | Required |
client_id | OAuth Client ID | Required |
client_secret | OAuth Client Secret | Required |
scope | OAuth permission scopes (leave blank unless required) | Optional |
verify_ssl | Enable/Disable SSL Verification | Optional |
http_proxy | Optional proxy configuration | Optional |
Fields with * marks are required.
- Click Create.
Troubleshooting
Authentication Failed (401 Unauthorized)
Verify that:
- The Client ID is correct.
- The Client Secret is correct.
- The API client has not been disabled.
- The Host URL points to the correct Taegis tenant.
Permission Denied (403 Forbidden)
Verify that:
- The API client has sufficient permissions.
- The requested OAuth scopes are allowed.
- Your organization permits API access.
Unable to Obtain OAuth Token
Verify that:
- The Client ID and Client Secret match.
- The OAuth client has not expired.
- The Host URL is correct.
- Network devices or proxies are not blocking outbound HTTPS requests.
SSL Errors
If SSL verification fails:
- Verify that the Taegis XDR endpoint uses a trusted SSL certificate.
- Confirm that any corporate proxy is not intercepting SSL traffic.
- Disable verify_ssl only for testing if permitted by your organization's security policy.
Result
You have successfully authenticated the SecureWorks Taegis XDR connector in Swimlane.
Sources
- SecureWorks Taegis XDR API Getting Started https://docs.ctpx.secureworks.com/apis/using_xdr_apis/
- SecureWorks Taegis XDR API Authentication Documentation https://docs.ctpx.secureworks.com/apis/authentication/
- SecureWorks Taegis XDR GraphQL API Documentation https://docs.ctpx.secureworks.com/apis/graphql/
- SecureWorks Taegis XDR API Reference https://docs.ctpx.secureworks.com/apis/